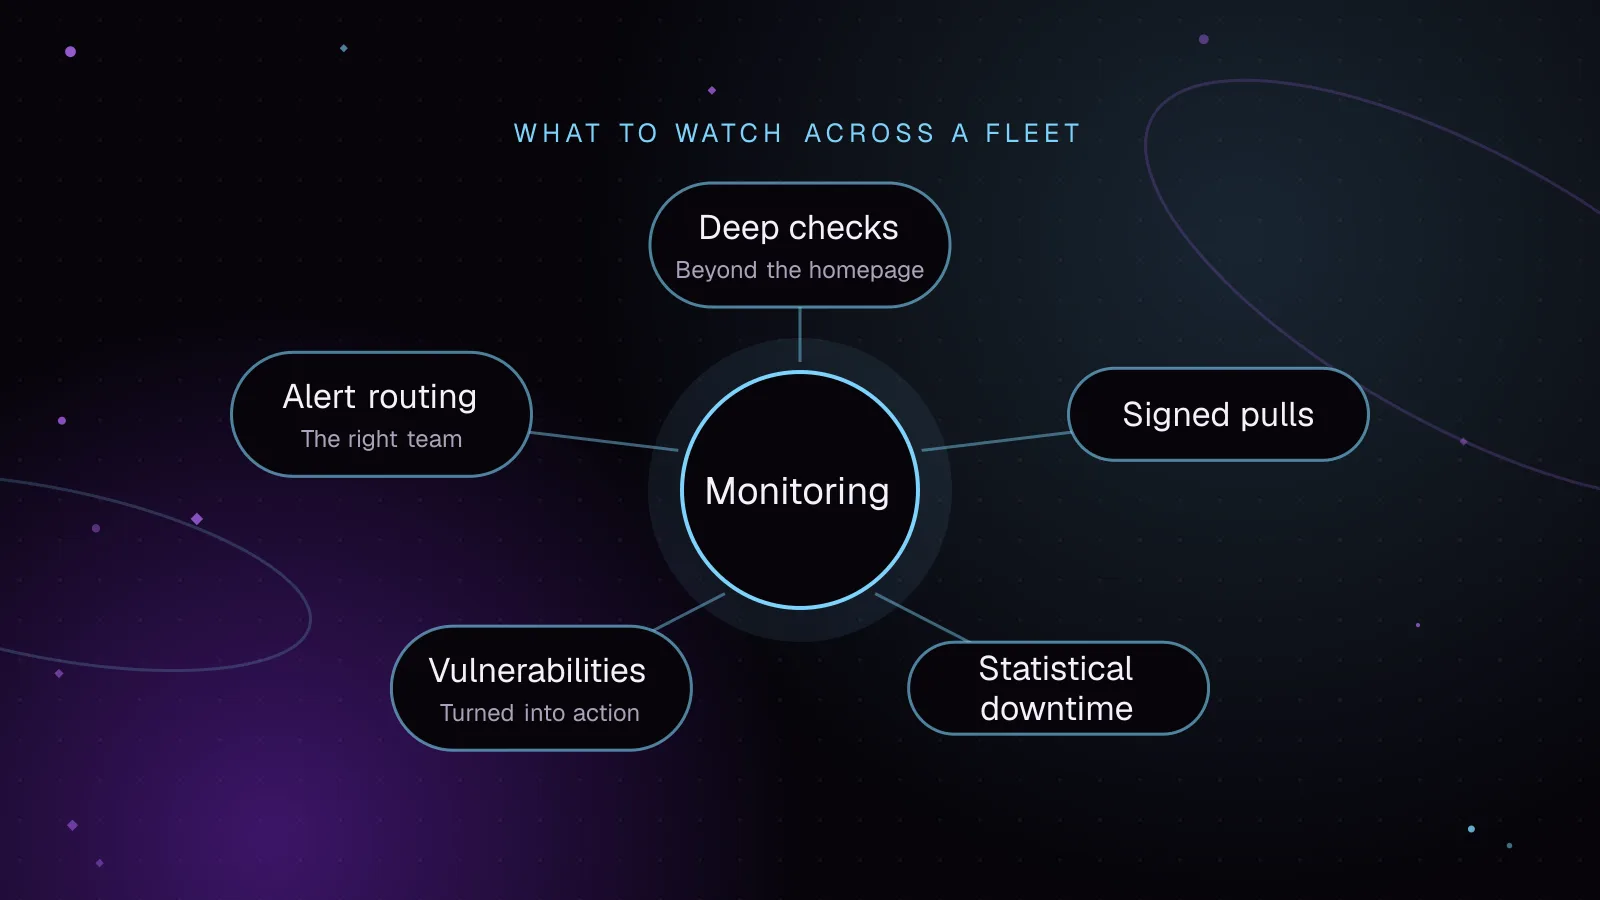
 Monitoring
5 min read
How to monitor WordPress sites without alert fatigue
Monitor WordPress sites with signed agent requests, vulnerability checks and alerts grouped by severity. Lessons from building Fleet Sentinel.
- WordPress
- Monitoring
- Security
10 articles
Every article tagged Security, newest first. Search all articles
Monitoring5 min read
Monitor WordPress sites with signed agent requests, vulnerability checks and alerts grouped by severity. Lessons from building Fleet Sentinel.
 Security
4 min read
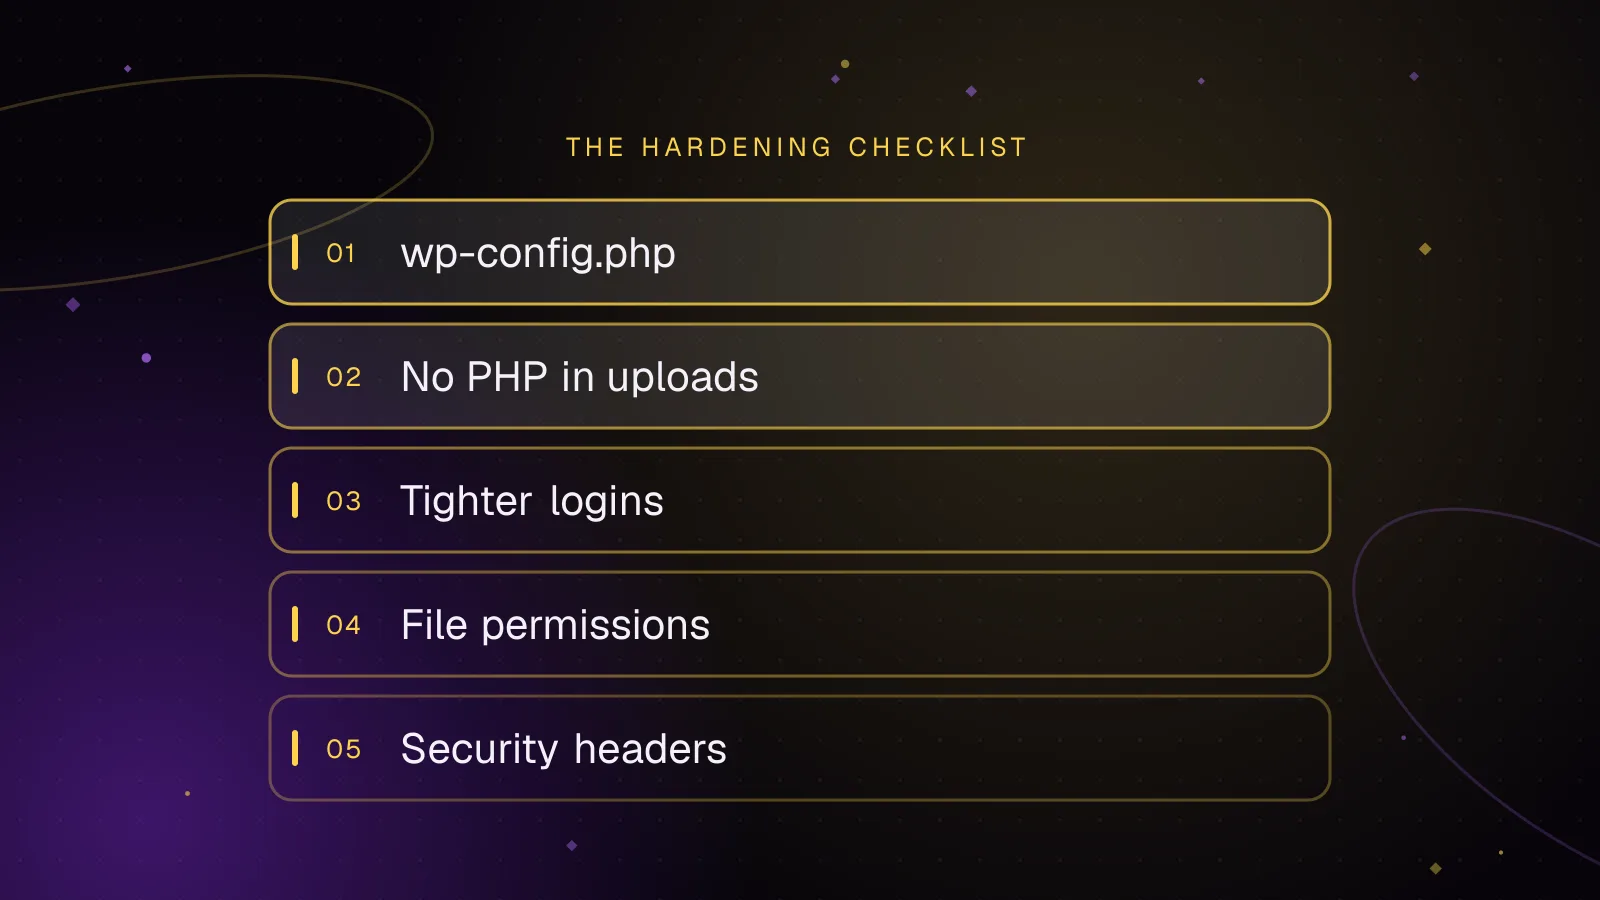
A practical WordPress security hardening checklist: updates, logins, wp-config settings, upload rules, headers and what to do after a hack.
 Security
7 min read
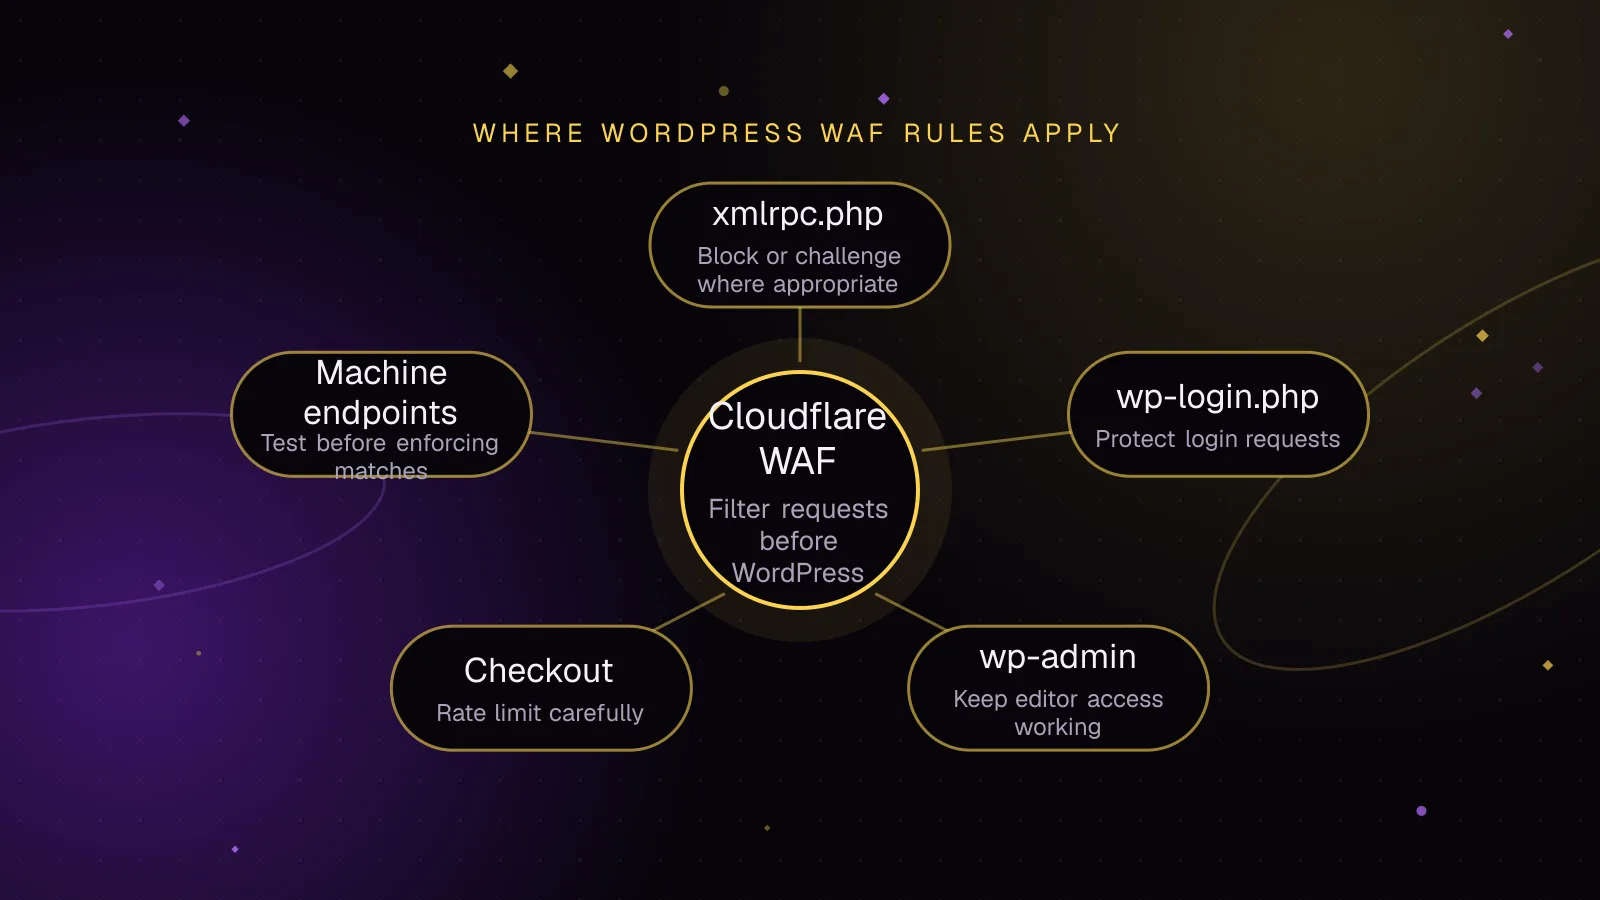
Use Cloudflare WAF rules WordPress sites can test safely, protect login and checkout paths, and avoid breaking webhooks, REST API traffic, or cron.
 Security
7 min read
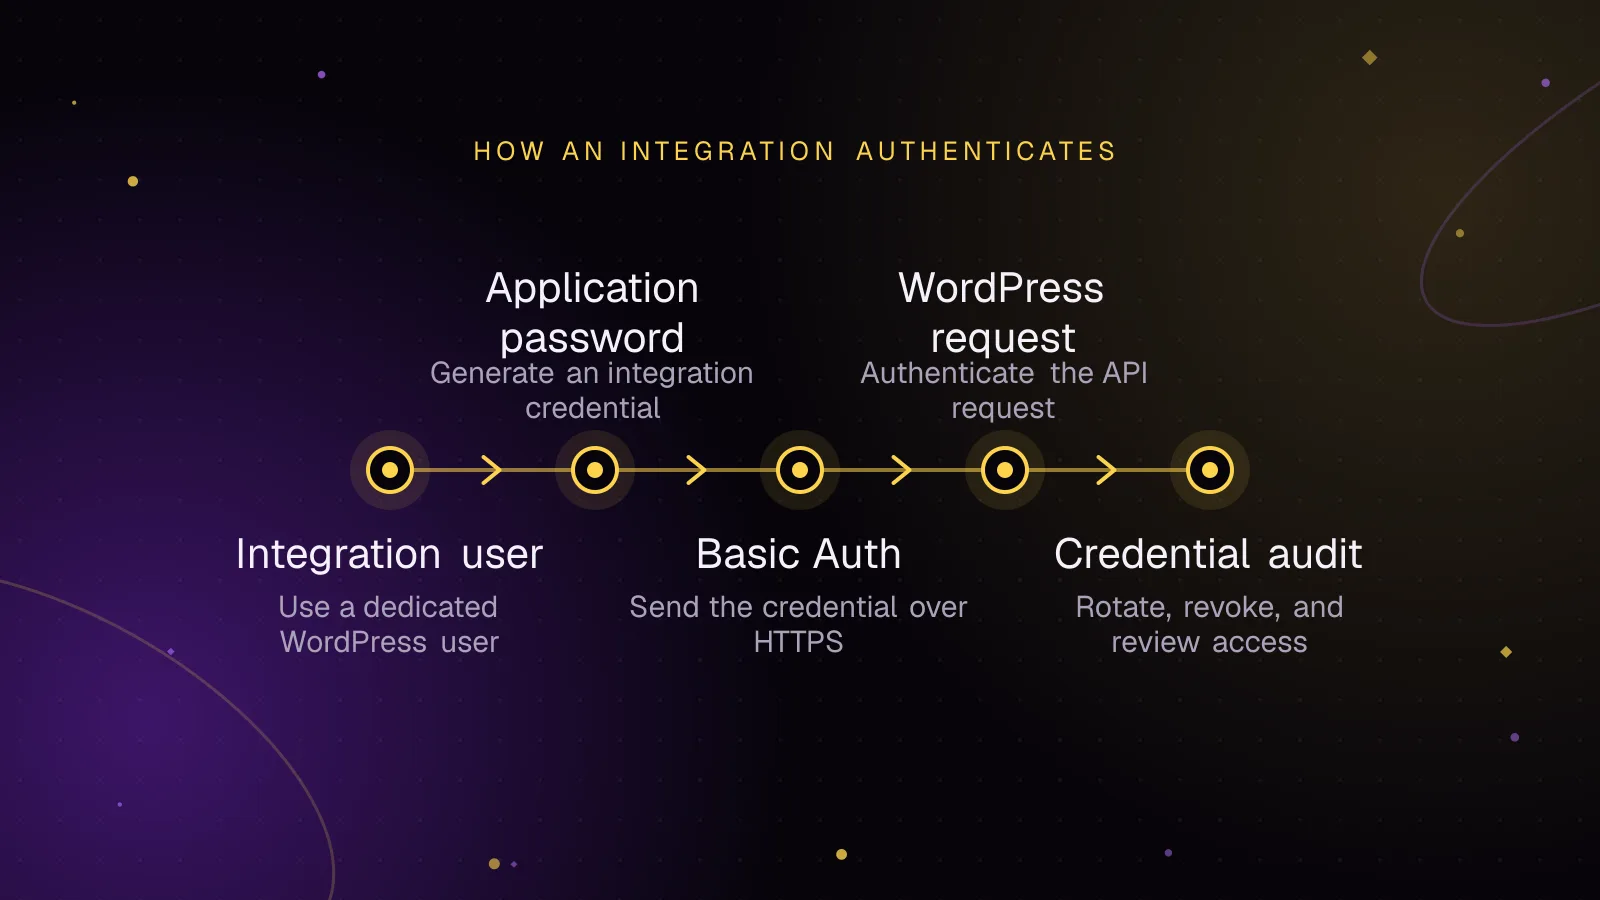
Use WordPress application passwords for REST API integrations with least-privilege users, HTTPS, rotation, revocation, and practical audit checks.
 Monitoring
8 min read
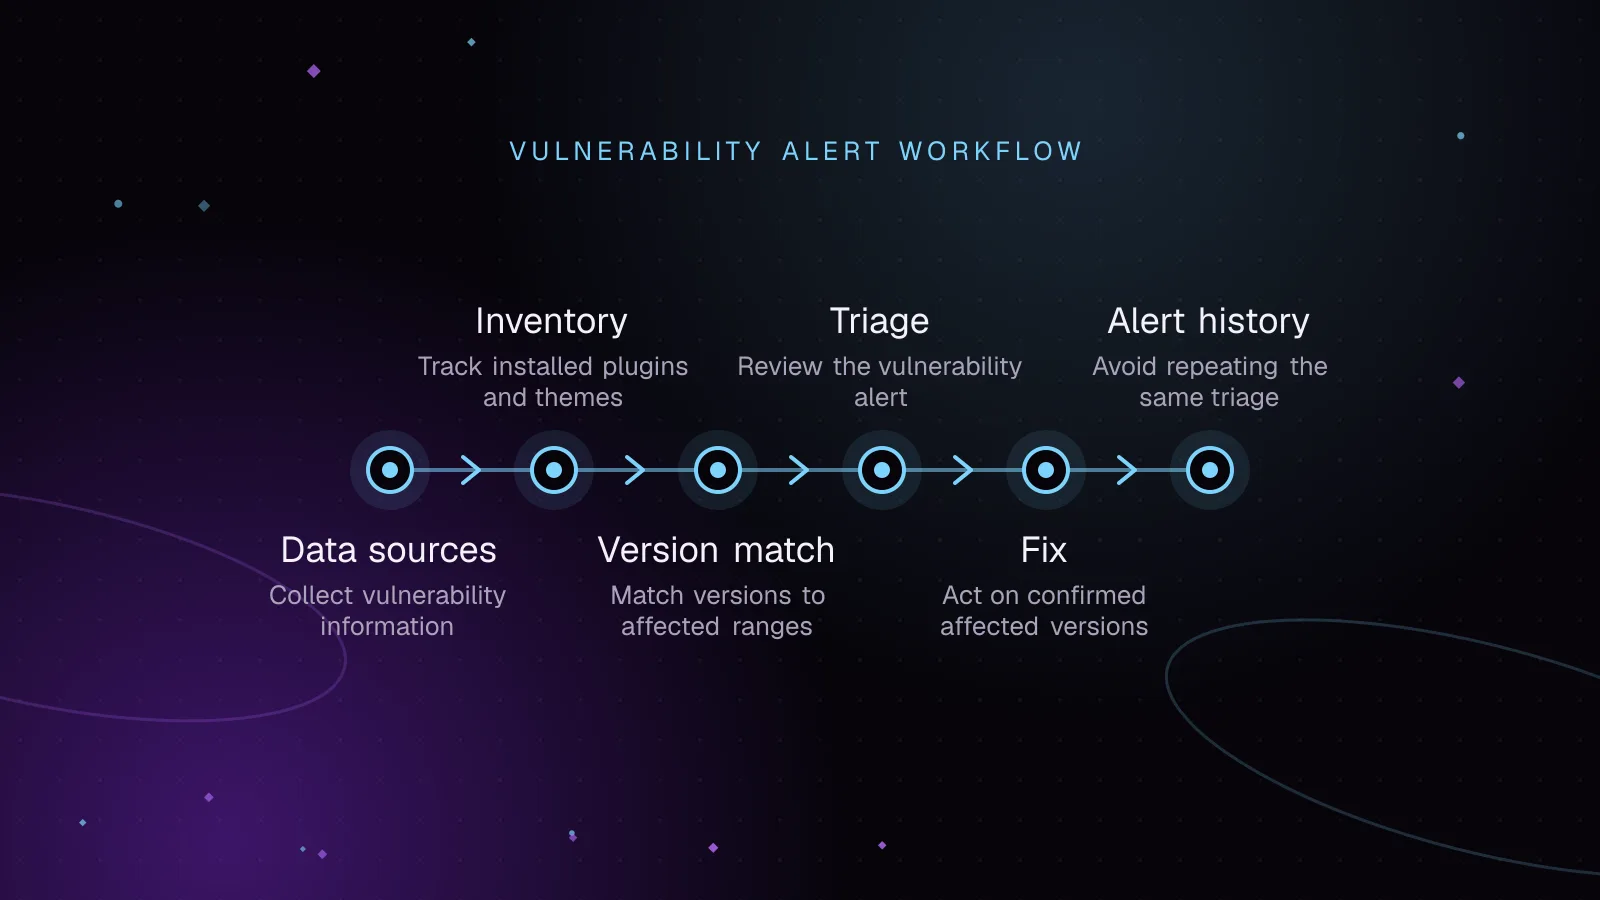
Use WordPress vulnerability monitoring to inventory plugins, match known flaws, triage risk, patch safely, and track closed or abandoned extensions.
 Security
8 min read
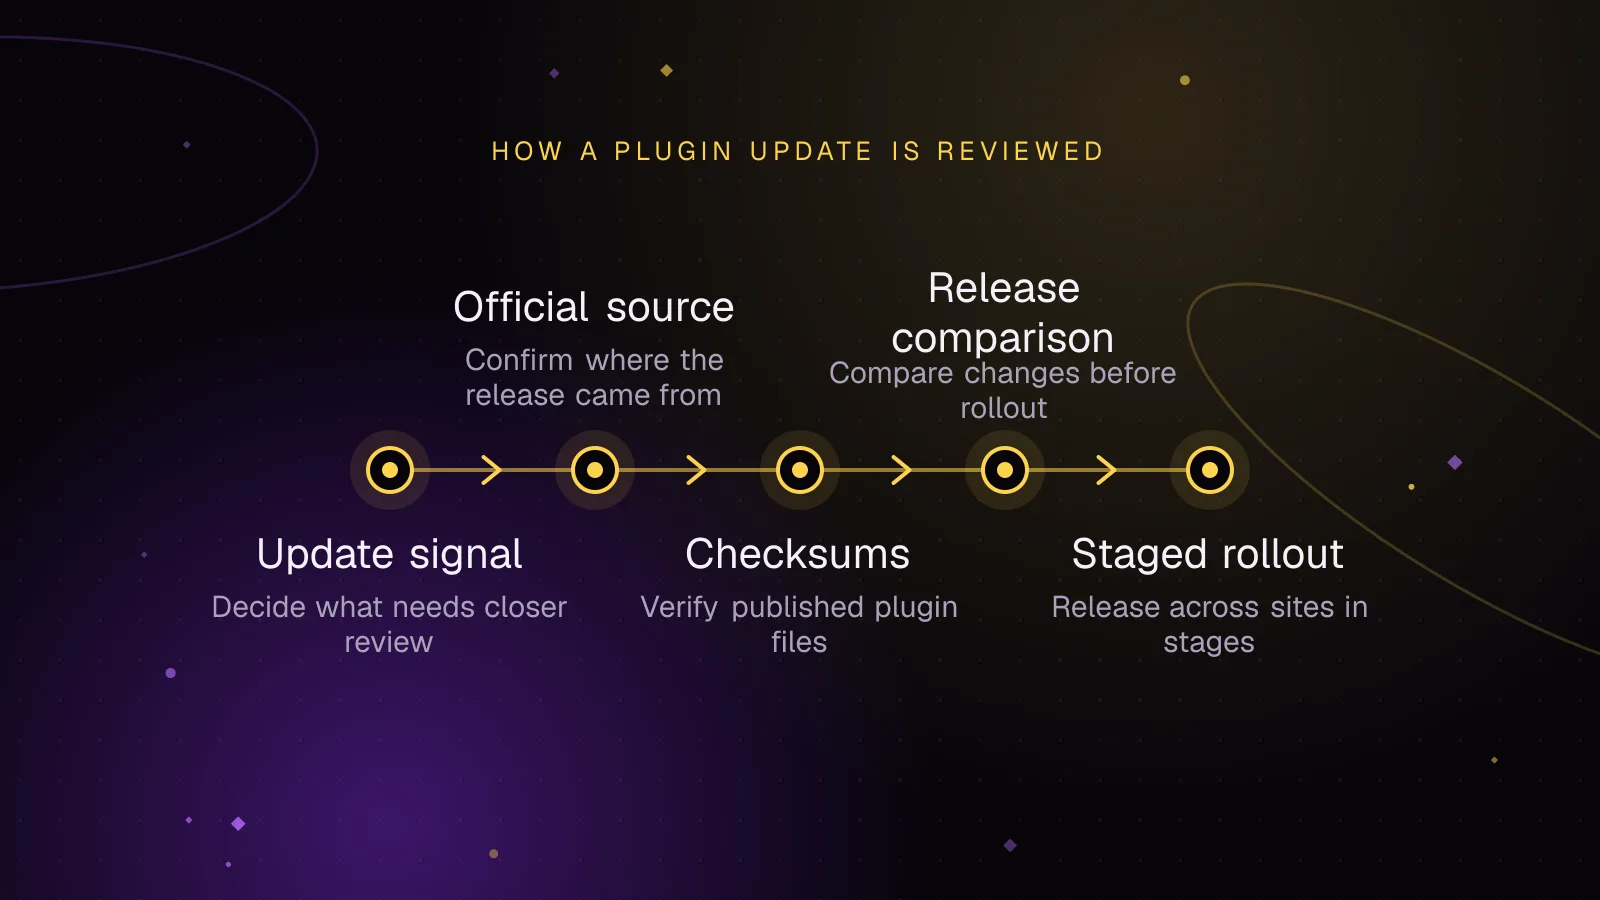
Use WordPress plugin supply chain security checks to verify updates, spot warning signs, stage releases, and respond fast to compromised code.
 Security
8 min read
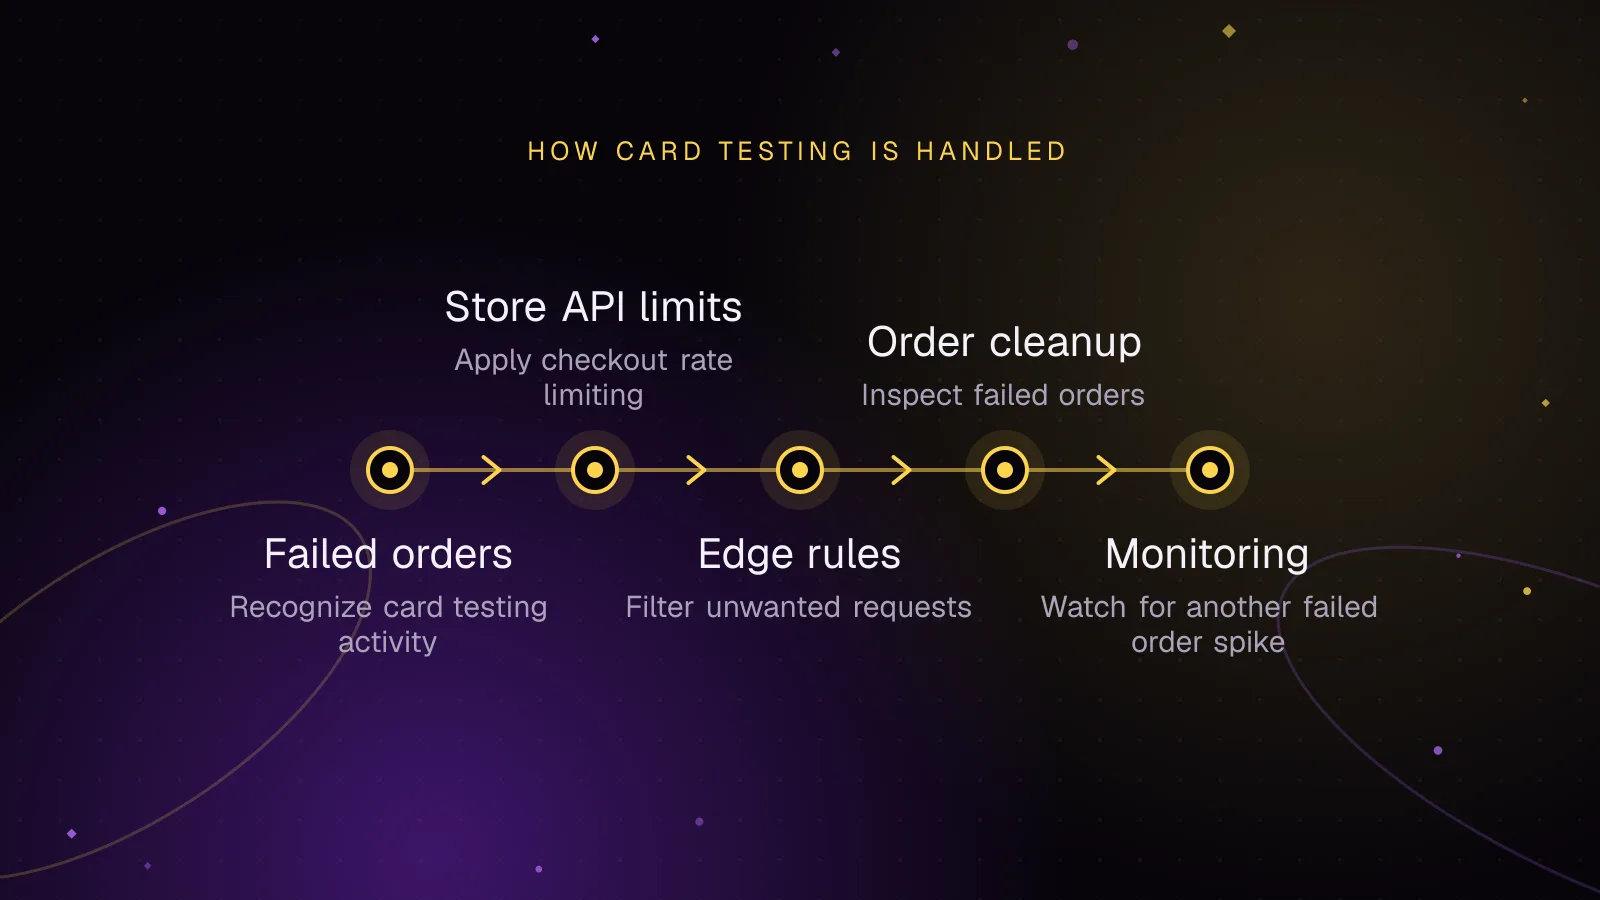
Stop WooCommerce card testing by spotting failed-order spikes, enabling Store API limits, tuning gateway fraud controls, and adding edge challenges.
 Security
7 min read
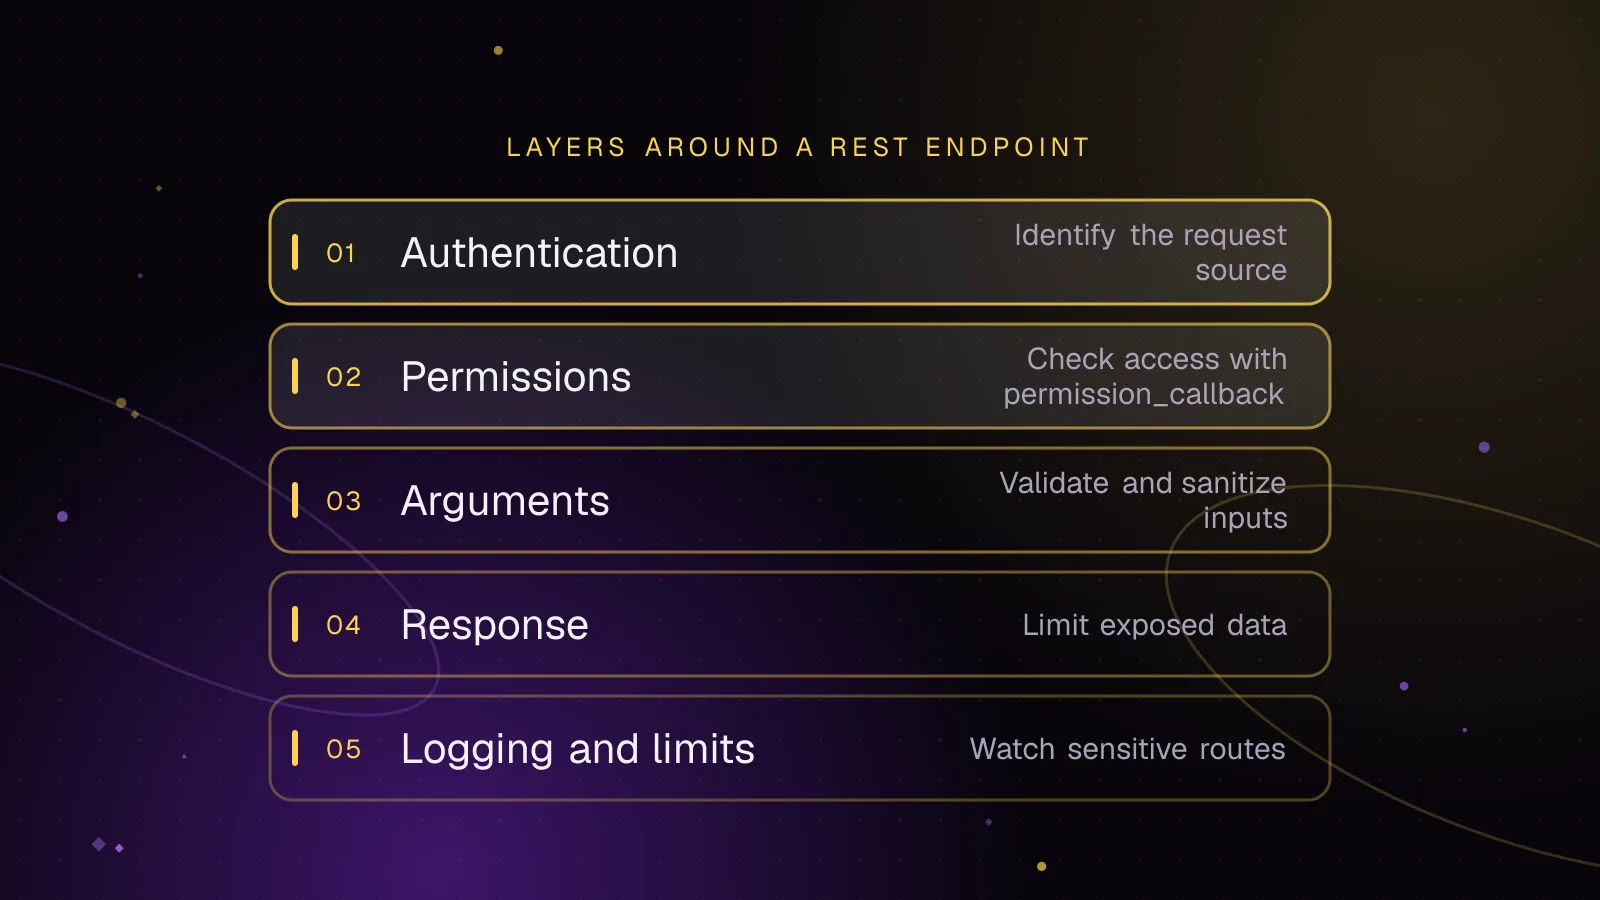
Review a WordPress REST API permission_callback, capability checks, nonces, argument schemas, output, logging, and rate limits for custom endpoints.
 Security
8 min read
Set WordPress security headers safely, test HSTS and CSP, avoid breaking WordPress, and verify every response with curl, DevTools, and Observatory.